Big News: Kosli’s achieves Series A milestone with Deutsche Bank as an investor - Read the announcement
New, open source: Explainable policies that run on Open Policy Agent and Rego. Explore ergo →
New: Kosli Answers is here! AI-powered insights for compliance and security. Learn more →

FeatureControl Center

Automated SDLC controls built for AI scale.

Control Center evaluates every SDLC event against your governance policies. Every control decision is automatic, recorded, and reproducible.

The problem

Human decision making doesn’t scale.

The AI SDLC demands automated, provable and reproducible decisions. With Kosli you can automate evidence evaluation and control decisions with policy-as-code.

Control gaps

When controls are only tested at audit time, gaps can go undetected until disaster strikes.

Delays and queues

As AI drives exponential change, manual approval decisions can't keep up.

Inconsistent decisions

Human evaluation can produce inconsistent decisions, especially at scale.

How it works

Trusted decisions for every control.

Control Center automates decisions for every SDLC event.
  1. 01Link controls to your enterprise risk management catalog.
  2. 02Define control requirements as Rego policies.
  3. 03Evaluate evidence in real time.
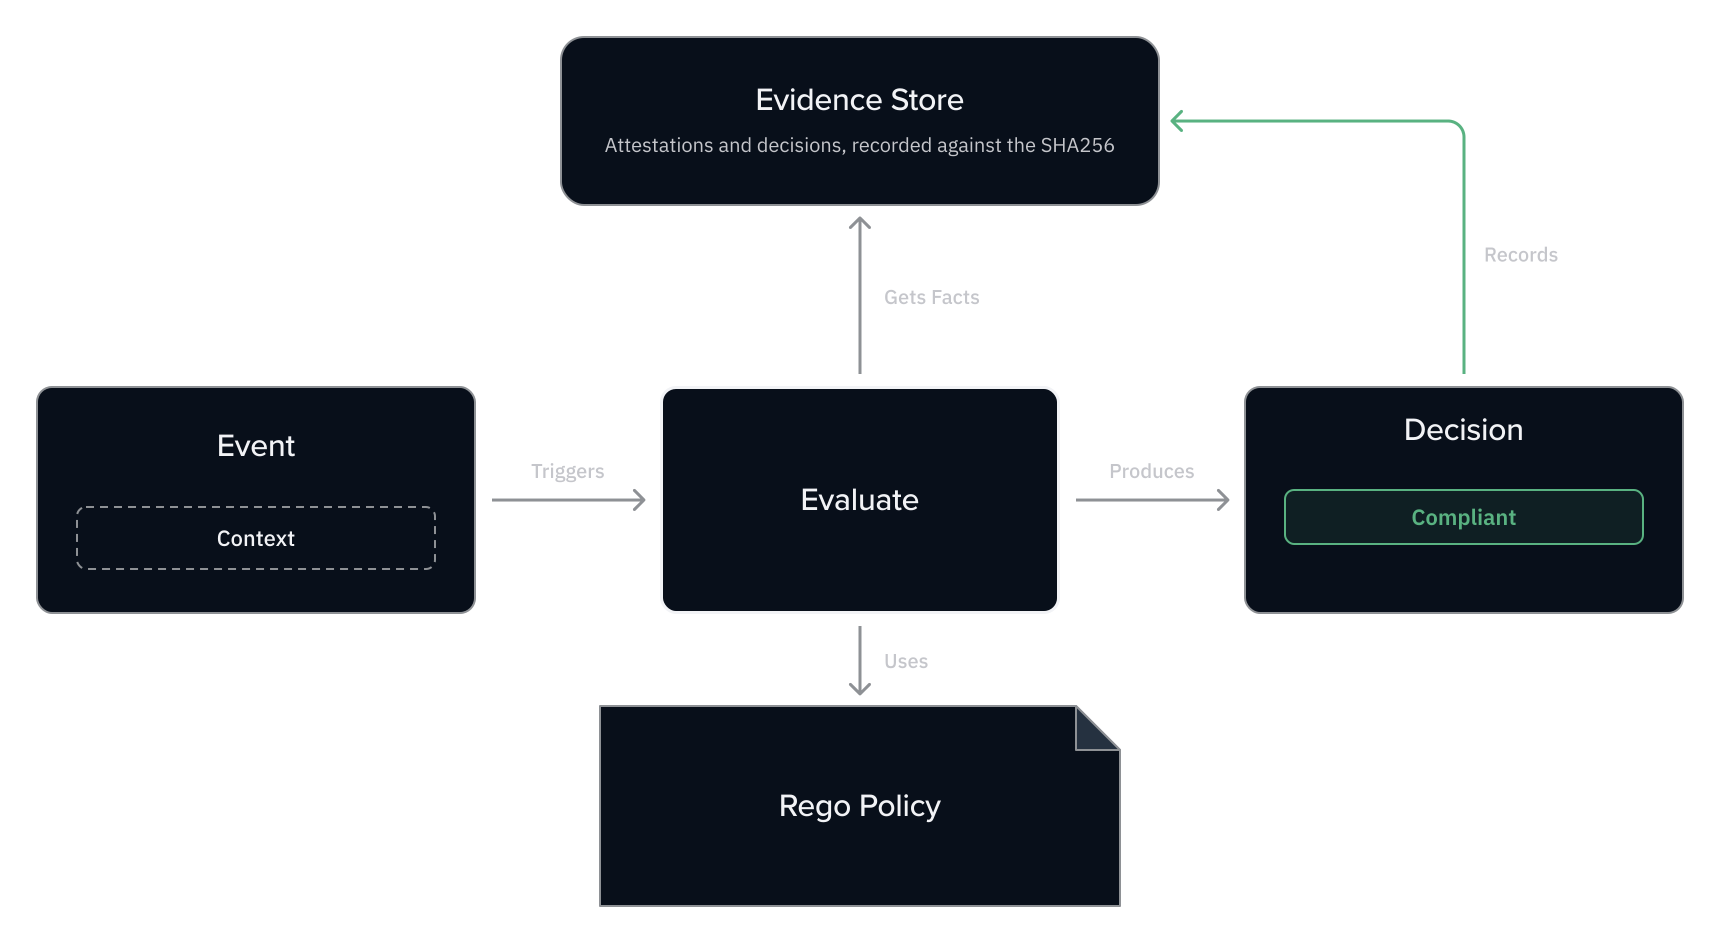
Control Center evaluation: an event, with its context, triggers an evaluation. Evaluate gets facts from the Evidence Store and uses a Rego policy, then produces a compliant or non-compliant decision. The decision is recorded back in the Evidence Store, alongside the attestations, against the artifact's SHA256.
Enterprise Scale

Bridging the gap between
enterprise governance
and software engineering

GRC reporting tools

  • ServiceNow
  • Archer
  • Databricks
  • Snowflake
  • etc…

Governance Operations

Control Center

Evidence store

Engineering toolchain

  • CI/CD tooling
  • Deployment tools
  • Cloud runtimes
  • Container runtimes
  • On-prem applications
  • Version control
  • Testing
  • Jira
  • Security tools
Coverage

Monitor compliance controls across the enterprise.

In practice

How to enforce a security requirement using Control Center.

Control

SAST Vulnerability Management

No change goes to production with known critical or high vulnerabilities.
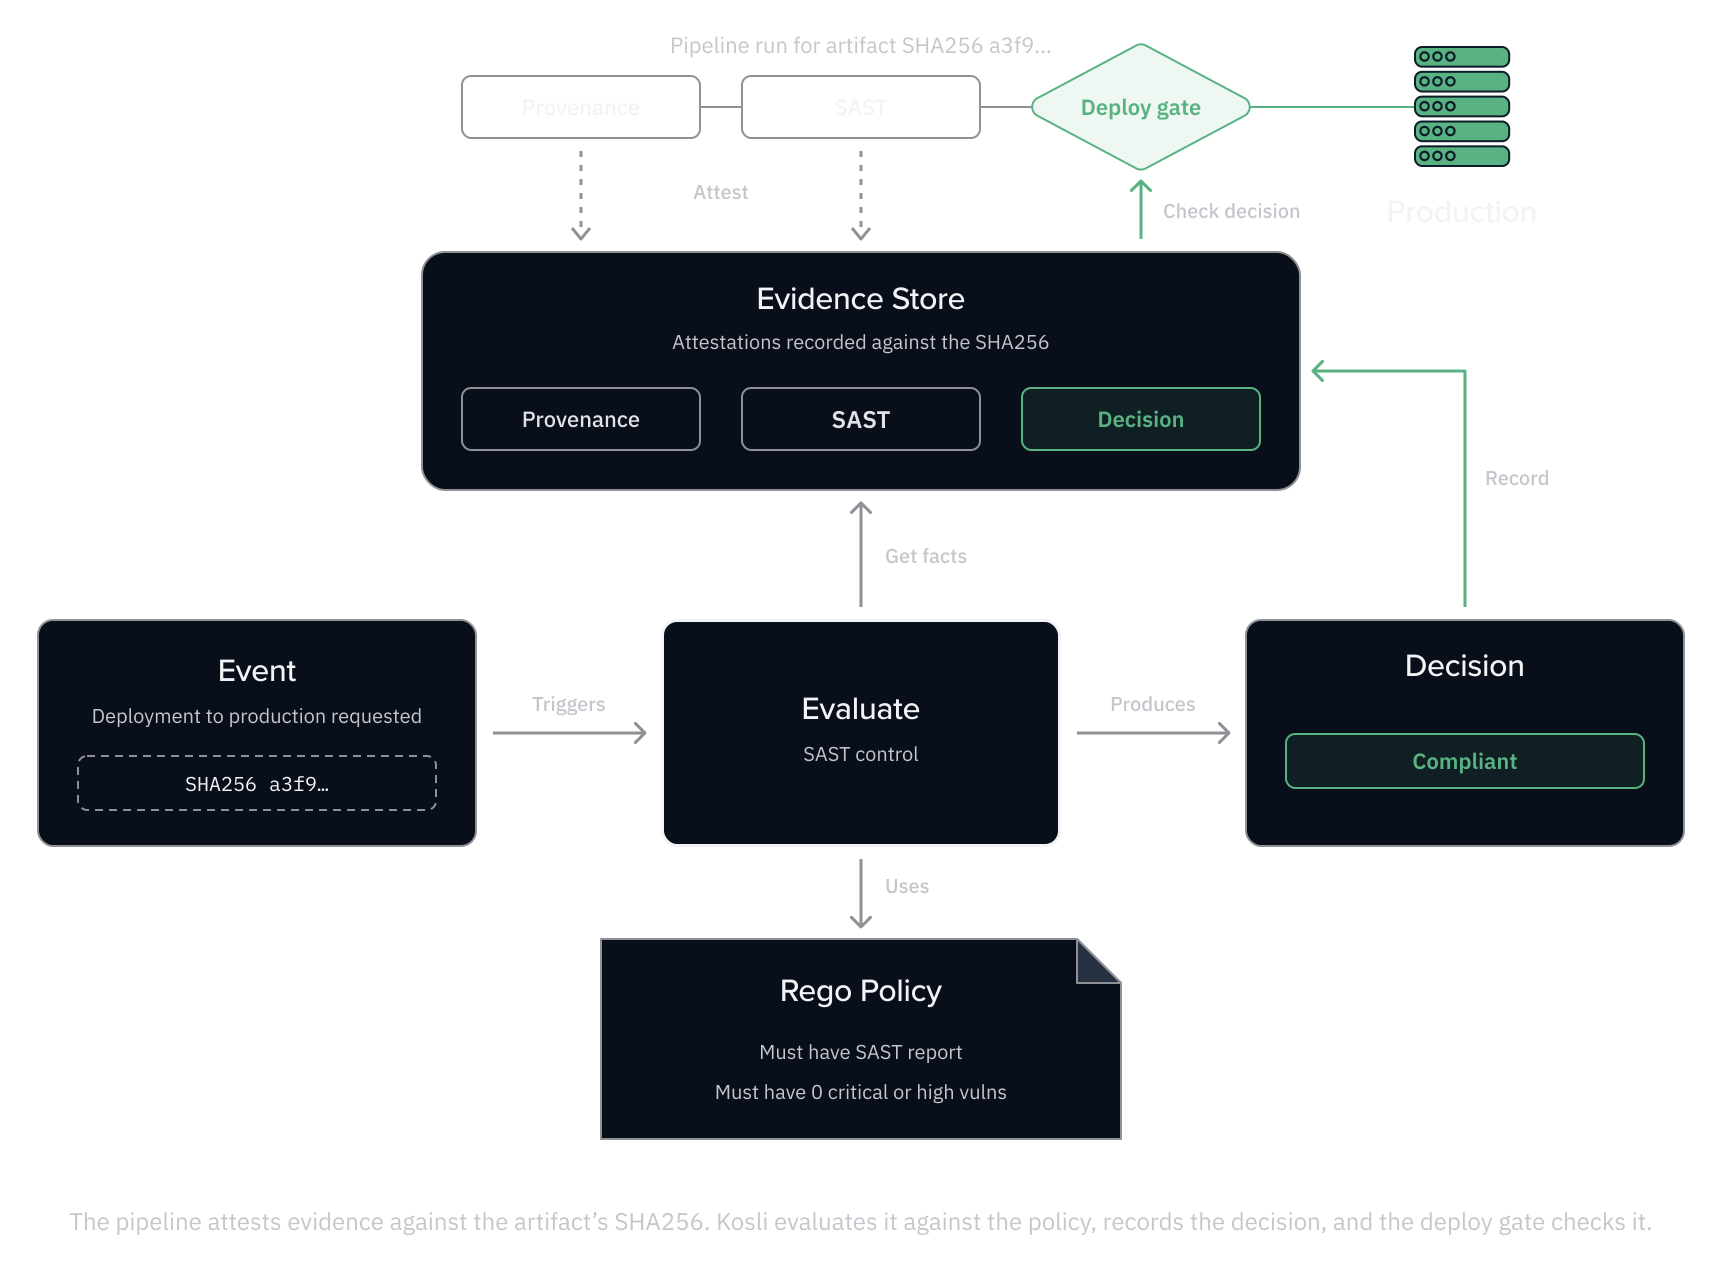
A pipeline run for an artifact attests Provenance and SAST evidence against its SHA256 into the Evidence Store. A deployment to production triggers Evaluate for the SAST control, which gets facts from the Evidence Store and uses a Rego policy (must have a SAST report, must have 0 critical or high vulnerabilities). It produces a Compliant decision, which is recorded in the Evidence Store, and the deploy gate checks that decision before the artifact reaches Production.

At build

Kosli records your security scan evidence in Evidence Store, cryptographically fingerprinted against the build and git commit fingerprints.

At release

Control Center evaluates your scan evidence using Rego. A non-compliant decision stops the deployment, a compliant decision lets it continue.

At audit

A report of all your control decisions, with accompanying evidence, is easily downloadable for you and your auditor.

Manual vs Kosli

Manual controls vs Kosli controls.

Manual controls Kosli controls
Evidence Gathered by hand, after the fact. Recorded at source, as it happens.
Decision A reviewer's judgment call. A Rego policy evaluated against facts.
Enforcement A sign-off in a meeting. A gate that acts on the decision.
Audit Rebuilt by hand, then sampled. Every decision, replayable.
Get started

Find coverage gaps in Kosli,
not in audit.

Watch it work, end to end

See the platform enterprise teams use to automate governance across build, release, and runtime.

Kosli in action