Big News: Kosli’s achieves Series A milestone with Deutsche Bank as an investor - Read the announcement
New, open source: Explainable policies that run on Open Policy Agent and Rego. Explore ergo →
New: Kosli Answers is here! AI-powered insights for compliance and security. Learn more →

EVIDENCE STORE

A trusted record of everything in your SDLC.

Governance starts with facts you can rely on. Kosli's Evidence Store is an append-only, immutable record of every event across your software delivery lifecycle.

SDLC Recording

Record and connect every event across your Agentic SDLC.

Attest. Connect. Search.

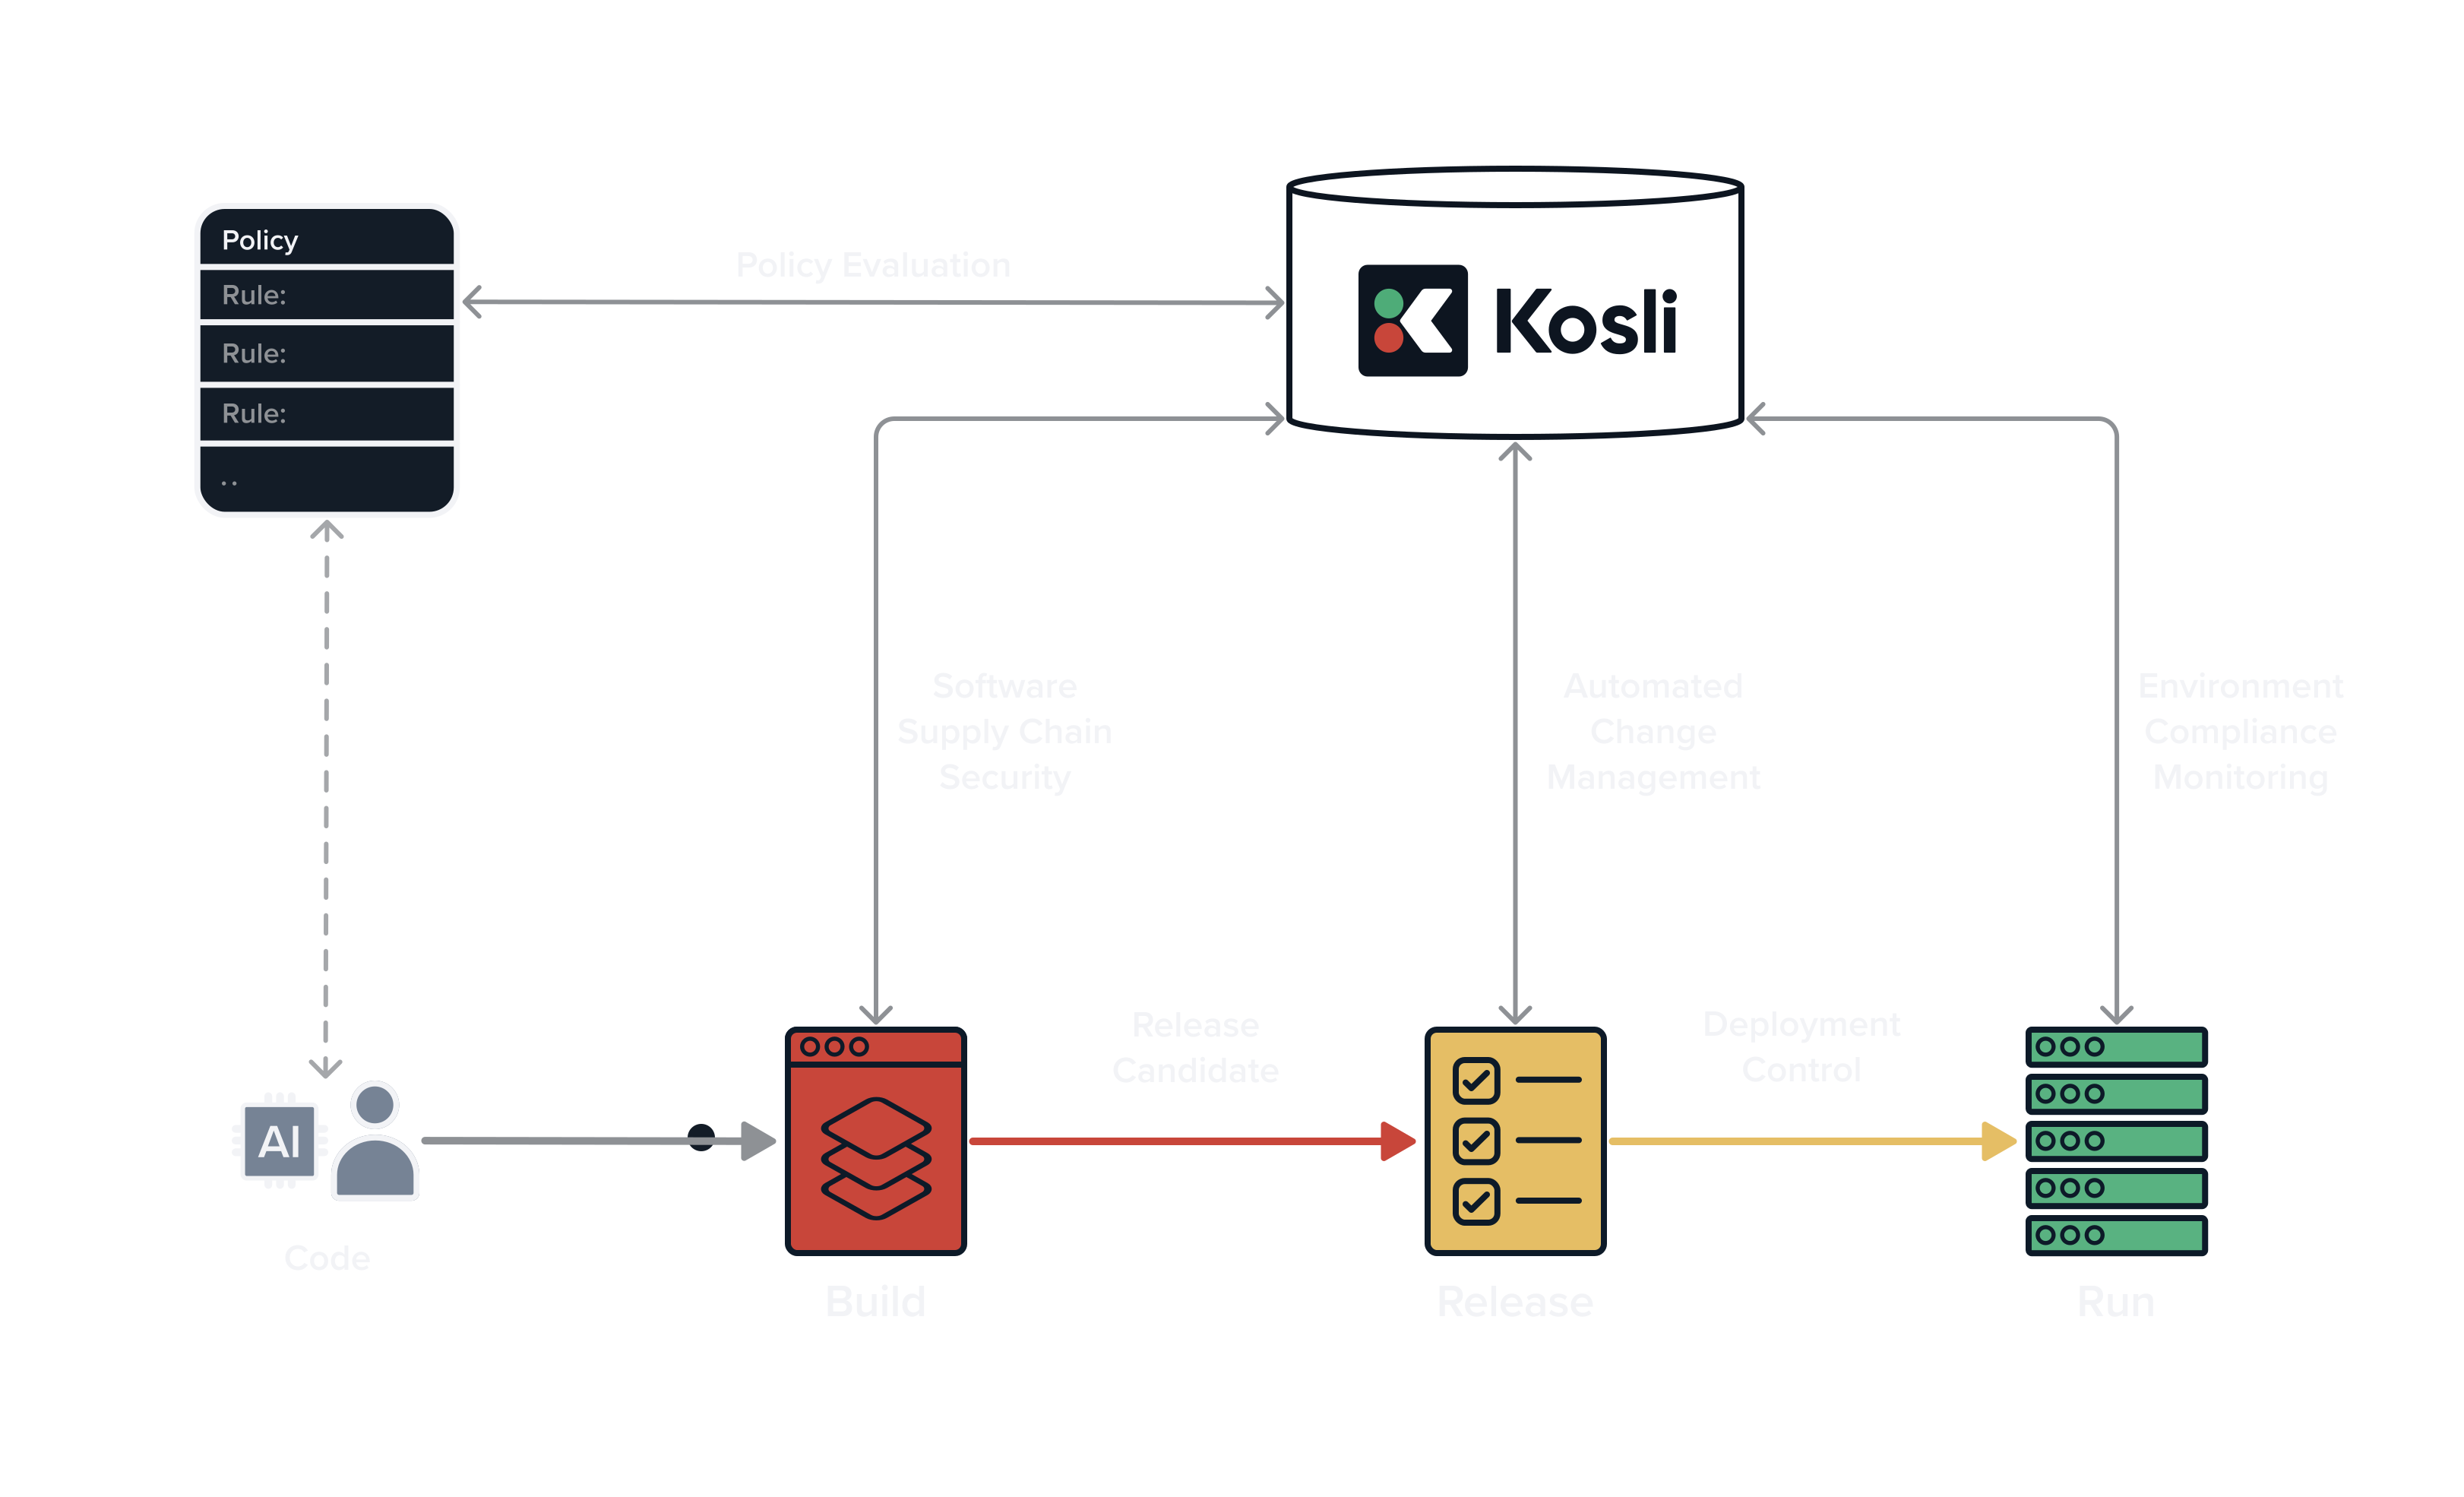
Automated SDLC governance is based on a factual record in Evidence Store. Pipelines attest to what they did, environments report what they are running, and both land in the same append-only record. Governance questions that used to need an investigation become simple search queries.
Attest
Builds, tests, scans, approvals
Connect
Runtime environments with pipeline runs
Search
Evidence trails, attachments, artifacts
Dive into all use cases
Kosli controls engineering map
Runtime recording

Every runtime change recorded and cryptographically tracked back to the commit.

A versioned history for every change to runtime

Kosli keeps an append-only history of runtime environments,
both on-prem and in the cloud.

Any environment type, any point in time. Kubernetes and ECS clusters, Lambdas, S3 buckets, Docker hosts, physical and virtual servers.
Every runtime workload is recorded cryptographically, so you can see exactly what was running last Tuesday at 14:02.

See workload compliance assurance
Diagram of kosli environment
Architecture

Record every event as a verifiable fact.

The foundation of governance is a trusted, central system of record. That's why the base of the stack is an append-only, immutable ledger of evidence.

GOVERNANCE OPERATIONS audit reports · dashboards · metrics CONTROL CENTER policy as code EVIDENCE STORE append-only immutable record CI / pipelines attestations tools / scanners attestations environments snapshots reads decisions export data · pdf enforcement gates · admission

Attestations and snapshots

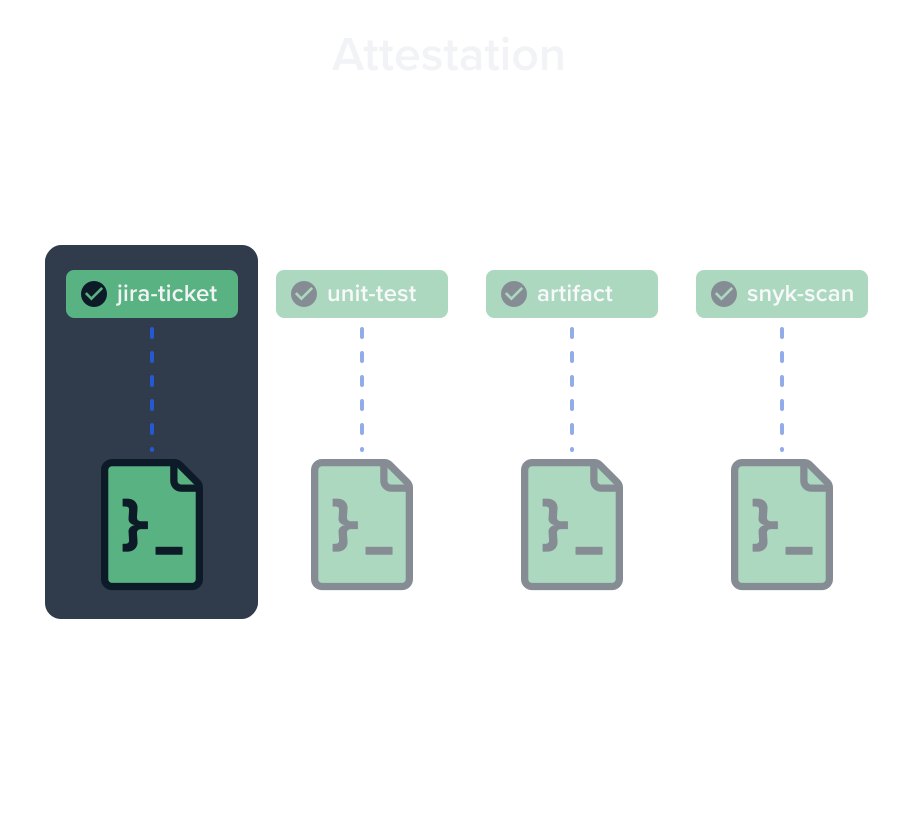
ATTESTATIONS: claims that an action happened (tests passed, a change was approved) and SNAPSHOTS: observations of the state of an environment.

Content Addressable Identities

Every artifact is identified by its cryptographic identity such as git commit or SHA256 checksum, not its name or tag. Evidence is connected via identities or correlation ids so that you can build a chain of custody from commit to production.

Append-only, independent record

The system of record has no update and no delete. A correction is a new fact, and the old one remains. Kosli holds the record outside your infrastructure, so altering history isn’t possible.

Flexible evidence types with schemas

Define the fact types your governance needs. Evidence that does not meet its schema is rejected at write time, and evaluated on ingest. Raw material (test output, SBOMs, scan reports) can be attached and fingerprinted in the Evidence Vault.

Kosli Concepts

Recording Your SDLC for Audit, Compliance and Security.

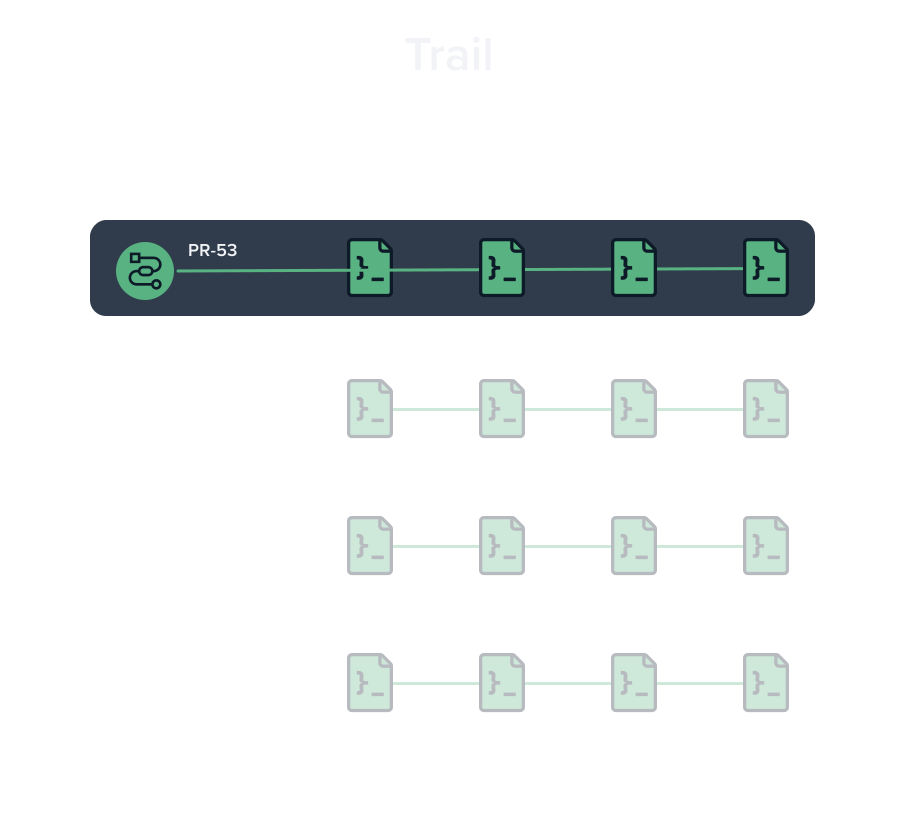
Trail: a chain of related attestations

Examples:

Diagram of kosli trails

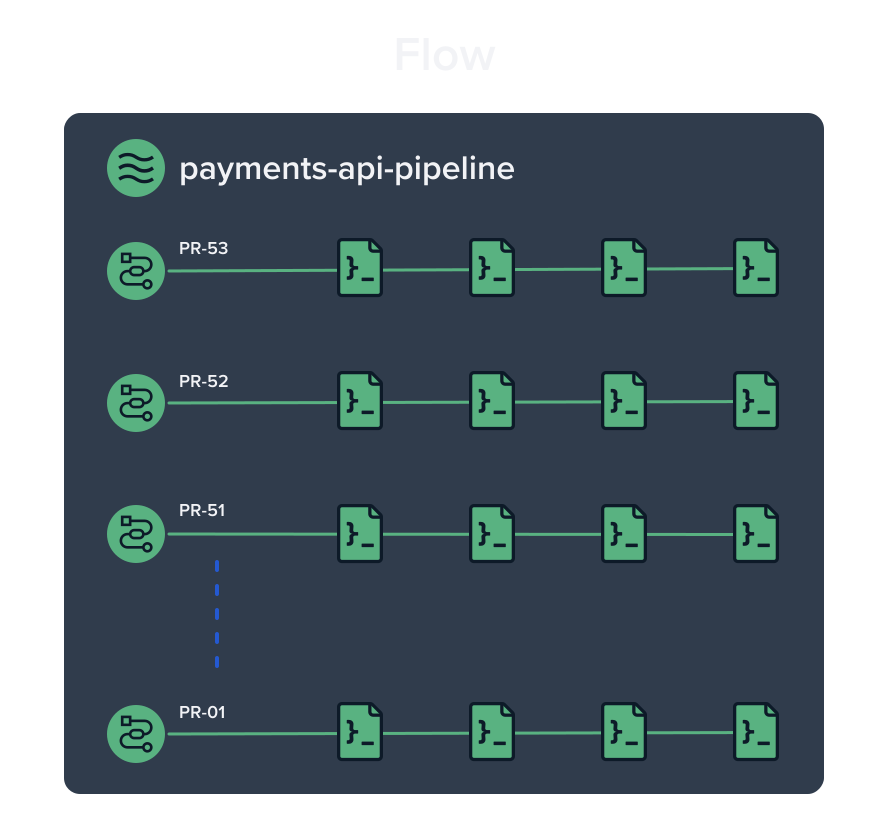
Flow: a collection of trails for a given process

Examples:

  • CI/CD runs for Payments api service
  • Terraform workflows for production account example
  • JIRA ticket development work
  • Feature flag changes
Diagram of kosli flows

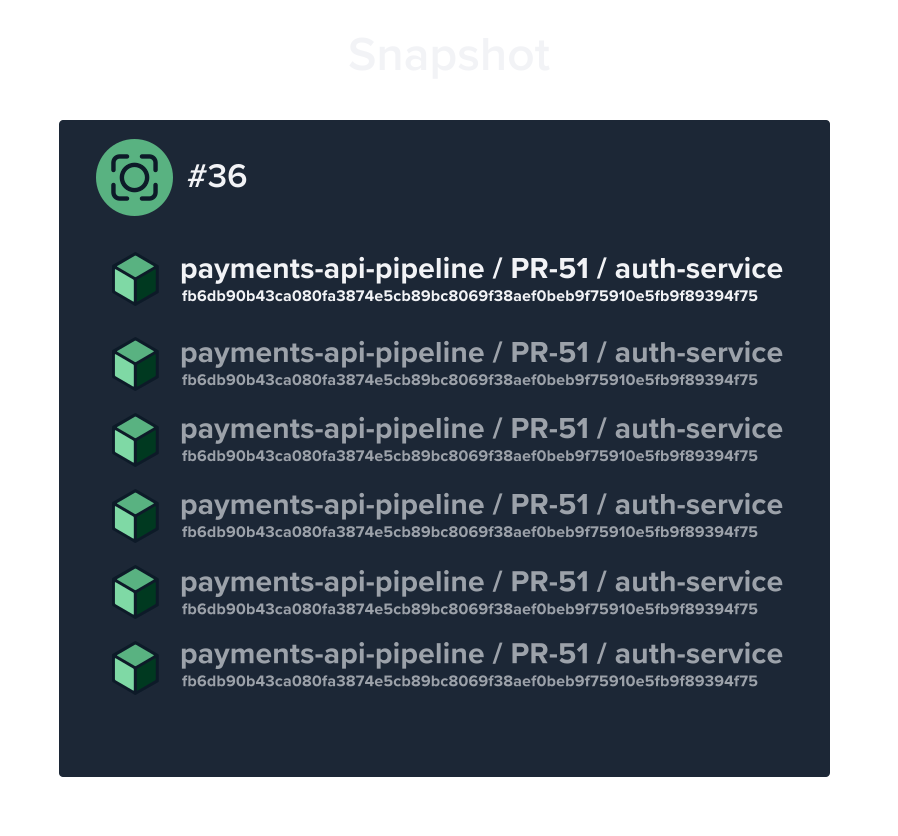
Snapshot: a record of the artifacts in a runtime system at a point in time

Examples:

  • The running artifacts in a AWS ECS namespace example
  • The running pods in a k8s cluster
  • The terraform state files in an S3 bucket
  • The functions in AWS Lambda
  • The files in a directory
Diagram of kosli snapshots

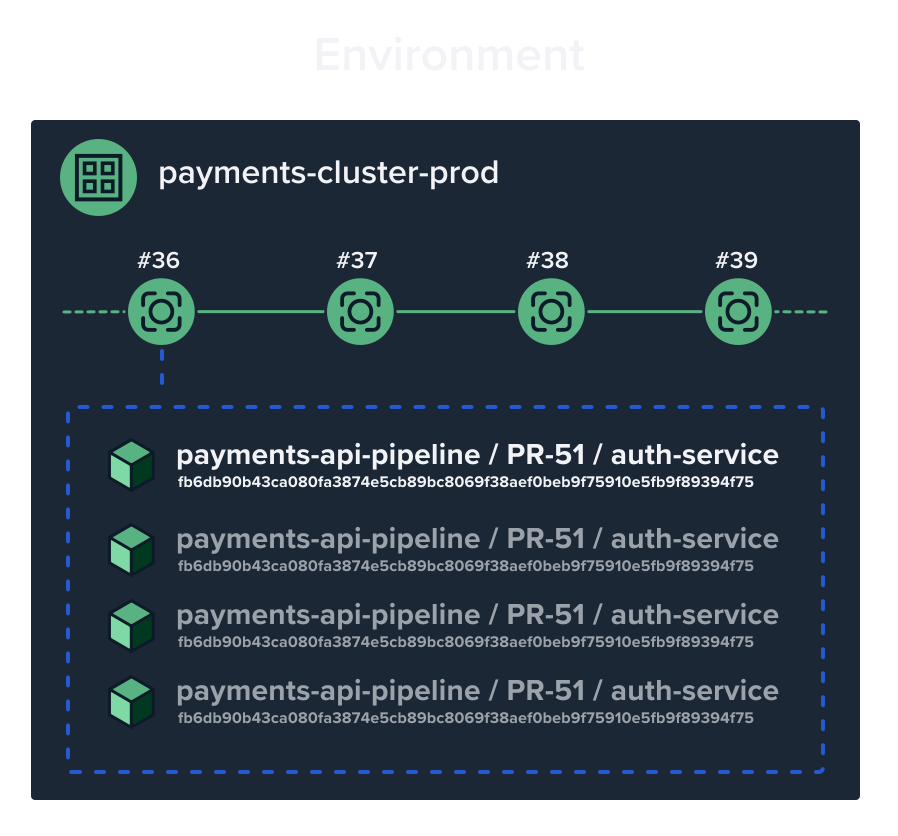
Environment: a history of snapshots for a runtime system over time

Examples:

  • How this k8s cluster changes example
  • How this S3 bucket changes
  • How this directory changes
  • How this lambda changes
Diagram of kosli environment

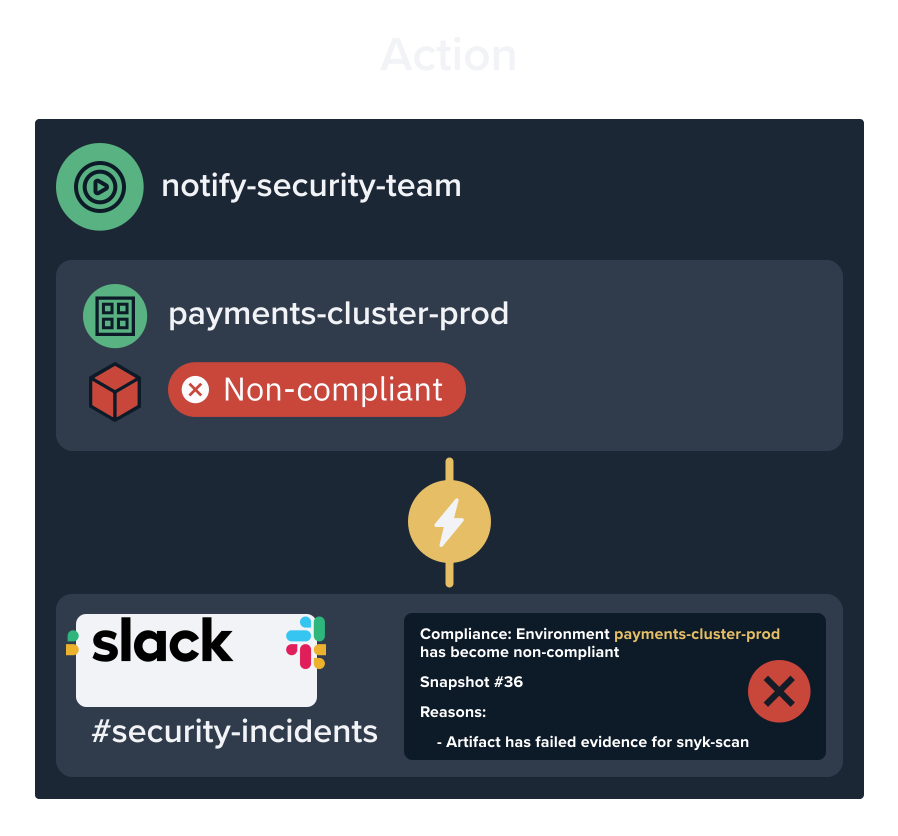
Action: trigger external systems based on changes

Examples:

  • Send a slack message when a deployment is detected
  • Start a CI process when an environment changes
  • Open an incident ticket when an unexpected change occurs
Diagram of kosli actions