Tags
Binary Provenance, SBOMs and the Software Supply Chain for Humans
“What’s really running in prod?” Every engineer will hear these immortal words on a long enough timeline (or career). It might be because a new security zero day was dropped, alerts fired from the …
Cybersecurity regulation and the software supply chain
It’s standard practice for software companies to use existing software components as building blocks for their new products. But what happens when those building blocks contain vulnerabilities …
How to secure your software supply chain with Artifact Binary Provenance
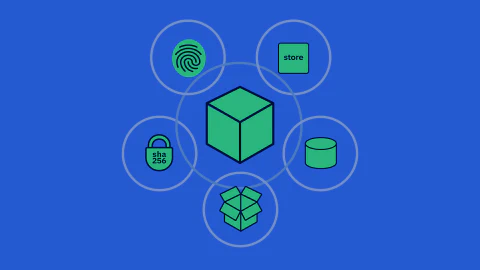
In Kosli, we use Artifact Binary Provenance as the foundation for our audit trails. Artifact Binary Provenance is a fancy term, but the idea behind it is really quite simple. All it means is that we …
Ready to ship at
AI speed, safely?
See how Kosli automates SDLC Governance inside your environment.
A Technical Guide to Controls Engineering
Free guide to SDLC Governance: automate compliance controls, eliminate change management bottlenecks, and deliver faster in regulated environments.
Download the guide


